AI-Driven Cyberattacks on Banks: CERT-In Alert
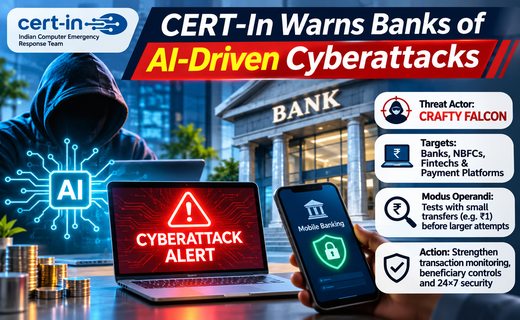
AI-Driven Cyberattacks on Banks are raising fresh cybersecurity concerns across India’s financial sector. A CERT-In advisory dated 4 November 2026 has been reported as highlighting threats to banks, NBFCs, fintech companies and payment platforms, although its full technical findings still require verification against the official document.
India’s banking and financial technology sector faces growing cybersecurity concerns as attackers adopt increasingly sophisticated techniques to target digital financial systems.
A 4 November 2026 advisory attributed to the Indian Computer Emergency Response Team (CERT-In) warns about AI-assisted cyber threats affecting banks, non-banking financial companies (NBFCs), fintech businesses and payment service providers.
The reported warning highlights the importance of protecting payment infrastructure, monitoring suspicious transactions and responding quickly to security incidents.
The official CERT-In advisory reference, CIAD-2026-0058, is the primary document for checking the agency’s exact findings and recommendations.
AI-Driven Cyberattacks on Banks: What Is the Concern?
Artificial intelligence can help cybercriminals automate parts of their operations, analyse stolen information and make fraudulent activity more difficult to detect.
The November advisory has been reported as identifying a threat actor called CRAFTY FALCON, associated with attacks against financial transaction systems.
Reported tactics include exploiting weaknesses in applications and payment interfaces to attempt unauthorised transfers.
However, the advisory’s complete technical findings could not be independently retrieved for this article. Specific attack descriptions should be confirmed against the original document before publication.
Why Payment Systems Are Attractive Targets
Banks and payment companies process large volumes of transactions through interconnected systems.
These systems depend on secure applications, access controls, payment interfaces and continuous monitoring.
If attackers compromise an authorised application or privileged account, they may attempt transactions that appear to originate from legitimate infrastructure.
The consequences can extend beyond financial losses to operational disruption, customer complaints and regulatory scrutiny.
Importantly, a cybersecurity warning does not establish that every bank or payment application has been breached.
Small Test Transactions and Larger Fraud Risks
One reported concern involves attackers using small-value transfers to test whether fraudulent payment instructions will be accepted.
Such activity may help criminals identify weaknesses in transaction controls before attempting larger payments.
For financial institutions, unusual transaction patterns deserve attention even when individual amounts appear insignificant.
Effective monitoring should consider transaction frequency, beneficiary changes, account behaviour and other indicators rather than relying exclusively on transaction size.
The precise transaction examples attributed to this campaign require confirmation from the advisory.
What Banks and Fintech Companies Should Do
Financial institutions can reduce exposure by strengthening several layers of security.
These include monitoring payment systems continuously, limiting privileged access, reviewing application vulnerabilities and maintaining effective incident-response procedures.
Additional safeguards may include stronger beneficiary verification, transaction limits, independent approval processes and alerts for unusual activity.
Institutions should also examine whether a security incident has been fully contained before restoring affected systems.
CERT-In maintains an official website for cybersecurity advisories and incident information, which organisations can consult alongside applicable regulatory requirements.
What Banking Customers Should Know
Customers should not assume that an advisory about financial infrastructure means their individual accounts have been compromised.
Nevertheless, basic precautions remain important.
Customers should enable transaction alerts, review account activity and avoid sharing passwords, PINs or one-time passwords.
Unexpected debit messages, unfamiliar beneficiaries or suspicious banking communications should be reported promptly through official bank channels.
Anyone who suspects financial cyber fraud in India can use the National Cyber Crime Reporting Portal or the 1930 cyber-fraud helpline.
Frequently Asked Questions
What are AI-driven cyberattacks on banks?
They are cyberattacks in which criminals use AI-assisted tools alongside conventional methods to identify weaknesses, automate malicious activity or support fraud attempts.
Does the warning mean all Indian banks are affected?
No. A sector-wide warning does not establish that every institution has suffered a breach.
What should customers do after noticing an unauthorised transfer?
Contact the bank immediately, request appropriate account safeguards and report suspected cyber fraud through official channels.
Conclusion
The reported CERT-In warning highlights the growing importance of cybersecurity across India’s banking and payment ecosystem.
Stronger monitoring, access controls and rapid incident response can help institutions manage emerging threats.
For customers, vigilance and prompt reporting remain essential.
Disclaimer: This article provides general cybersecurity information. It does not confirm a breach at any specific bank or replace official regulatory or security guidance.